Politics
Hackers Put 41,000 DHS Agents, Contractors At Risk After Major Breach
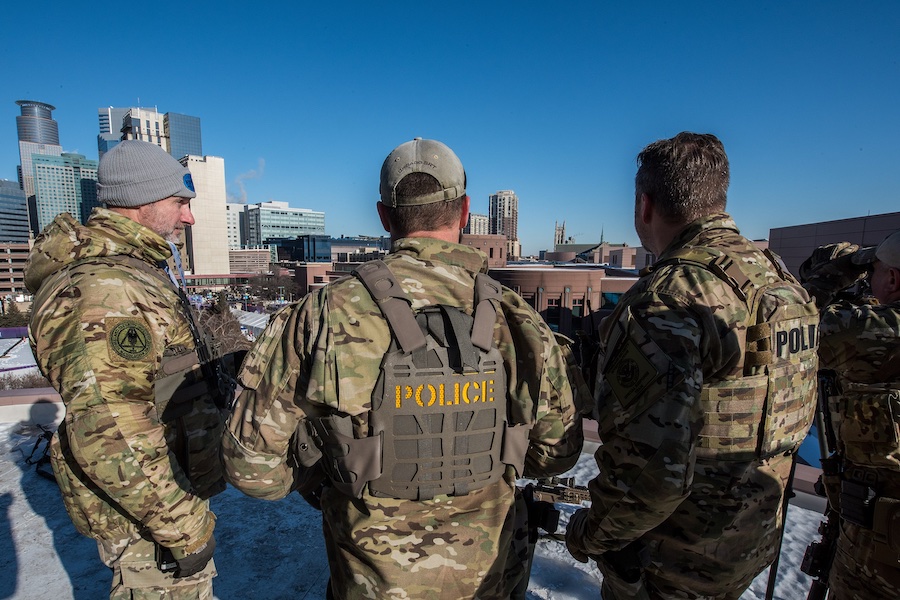
Hackers have exposed the identities and contact information of more than 41,000 Department of Homeland Security employees and contractors in a massive data breach that could put federal immigration officers, undercover investigators and their families at risk.
The stolen information surfaced Wednesday in a searchable online database containing records tied to Immigration and Customs Enforcement, Customs and Border Protection and other DHS agencies.
The Washington Post reported that current and former Homeland Security officials verified the authenticity of the exposed records, raising concerns about the potential consequences for federal law enforcement personnel.
A self-described hacktivist group calling itself the Department of Peace claimed responsibility for accessing the information through a single sign-on service used by DHS employees to enter internal systems.
The group reportedly transferred the records to Distributed Denial of Secrets, a nonprofit that publishes leaked government documents, and Swiss hacker maia arson crimew.
The information was subsequently organized into a database called Icepick, allowing users to search employee names, offices, contact information and assignments.
The breach comes as President Donald Trump’s administration continues its sweeping immigration enforcement operations, placing federal agents at the center of an increasingly contentious national debate.
Homeland Security officials have repeatedly warned that immigration officers face threats, harassment and potential violence because of their enforcement duties.
Now, the exposure of thousands of personnel records threatens to create additional security risks for employees whose identities were previously shielded from public disclosure.
DHS acknowledged the incident Wednesday evening, confirming that officials were investigating a potential security breach.
🔥🚨 BREAKING: A Left-Wing hacking group broke into the U.S. Department of Homeland Security’s personnel files and exposed the names, phone numbers, and addresses of more than 40,000 DHS agents
The left-wing group calling itself the “Department of Peace” claimed they got in by subverting DHS’s single sign-on system.
Handed the data to Distributed Denial of Secrets, which posted it in a database called Icepick. More than 21,000 records are CBP employees and another 10,000 are ICE and HSI.
DHS says it is aware of a potential breach and working to address it. The hackers tied it to earlier comments from Markwayne Mullin about turning up the heat on ICE.
This is an unprecedented dump of sensitive personnel data.
— The Patriot Oasis™ (@ThePatriotOasis) October 29, 2026
The agency said it was “aware of a potential breach” and was “working to address the situation swiftly and effectively.”
“We take all security threats against our employees and officers seriously and will work to ensure all are properly protected. We will update the public when more information is available,” DHS said.
The hacking group claimed its actions were intended to increase transparency surrounding federal immigration operations.
However, a statement accompanying the leaked material directly referenced Homeland Security Secretary Markwayne Mullin and the administration’s immigration crackdown.
“On July 17th, Markwayne Mullin said he was ‘turning up the heat,’” the group wrote.
“This is what happens to ICE when you do that.”
POLL: Should Migrants Who Murder Americans Face The Death Penalty?
The apparent targeting of immigration enforcement personnel has alarmed former senior officials, including those who served under Democratic administrations.
John Sandweg, who led ICE on an acting basis during former President Barack Obama‘s administration, described the exposure as a “nightmare scenario.”
Sandweg warned that publishing the identities of federal agents could put them “in great jeopardy” while potentially compromising investigations into dangerous criminal organizations.
“I feel terrible for the agents and their families,” Sandweg said. “The array of threats they face as a result of this is stunning.”
Those concerns extend beyond immigration enforcement operations.
RELATED: NEW: DHS To Test ‘Heat Ray’ Weapon For Potential Use At US-Mexico Border
Homeland Security Investigations personnel conduct investigations involving transnational gangs, drug trafficking networks and other criminal organizations, making the disclosure of certain assignments particularly sensitive.
According to the Washington Post, an intelligence unit within Homeland Security Investigations distributed a warning to agents following the breach.
Yet several ICE officers and Border Patrol agents contacted by the newspaper said they had not received official notification about their information being exposed.
The disclosure also raises fresh questions about the security of federal computer systems.
Just weeks earlier, another hacking organization claimed to have obtained thousands of FBI employee records, prompting concerns about personal information potentially reaching foreign intelligence services or criminal groups.
Meanwhile, the organizations responsible for publishing the DHS database defended their decision, arguing that the public should have greater access to information about immigration enforcement operations.
RELATED: DHS Secretary Mullin Give Cryptic Statement On Ilhan Omar Case: ‘Multiple Warrants’
“Rather than an indiscriminate directory of every DHS employee, Icepick identifies many of the architects and drivers of DHS policy and operations,” Distributed Denial of Secrets co-founder Emma Best said.
The nonprofit maintained that the database could help researchers examine the backgrounds of officials involved in federal immigration policy and undercover operations.
But exposing agents’ identities also carries potential consequences for their personal safety, particularly amid ongoing threats against immigration enforcement personnel.
DHS has defended officers who wear masks during enforcement operations, saying the practice helps protect them and their families from retaliation.
The hackers acknowledged that their database does not contain every DHS employee and may include inaccurate information.
Officials have not publicly determined the full scope of the intrusion or whether the exposed records have been used to threaten individual employees.
